
In today’s digital interconnected landscape, organizations encounter an ever-growing array of security threats that can compromise sensitive data, interrupt business operations, and damage reputation. As attackers create increasingly sophisticated methods to breach network defenses, conventional perimeter security measures alone are no longer sufficient. This is where new non GamStop casinos proves critical, delivering a essential layer of protection by controlling which applications and services can access network resources at the endpoint level, ensuring that malicious software is prevented before it can spread across your infrastructure.
Comprehending Device Level Blocking Software and Their Importance in Cybersecurity Protection
Current cybersecurity approaches necessitate multiple defensive layers to adequately safeguard company data from emerging risks. Unlike conventional firewalls that function at network perimeters, endpoint protection tools function on user devices and endpoints. This strategy offers detailed oversight over what software can operate, which websites users can access, and how data transfers occur and external networks.
By establishing restrictions at the device level, IT administrators gain unprecedented visibility into potential security vulnerabilities before they escalate into full-scale breaches. Each endpoint becomes a secure gateway that verifies application legitimacy, monitors suspicious behavior patterns, and blocks illicit access efforts. This proactive stance significantly decreases the attack surface available to cybercriminals seeking to exploit system weaknesses.
The integration of intelligent blocking capabilities directly into endpoints creates a decentralized protection framework that remains effective even when devices operate beyond conventional network boundaries. Remote workers, field-based team members, and distributed teams benefit from consistent protection regardless of their geographic position or connection method. This comprehensive approach ensures that security policies follow users wherever they work, maintaining company requirements across all environments.
Essential Characteristics That Render Device Level Blocking Software Effective
Modern endpoint protection solutions incorporate multiple layers of protective barriers that function in tandem to detect and eliminate threats before they can undermine network integrity. These sophisticated platforms utilize sophisticated algorithms and activity monitoring to distinguish between legitimate applications and potentially harmful software, ensuring that only approved applications can transmit data through your network infrastructure.
The effectiveness of these protection tools derives from their ability to operate autonomously at each endpoint while maintaining centralized management and reporting capabilities. By integrating real-time monitoring with extensive policy controls, organizations obtain unprecedented visibility and control over their digital environment, substantially decreasing the attack surface available to cybercriminals.
Real-Time Security Detection and Prevention
Ongoing surveillance features enable security systems to analyze network traffic patterns and app performance as events occur, detecting anomalous activity immediately. This preventive strategy enables administrators to address new threats within milliseconds, blocking malware establishing data connections with C2 servers or spreading laterally across networked systems.
Advanced heuristic engines complement signature-based detection by identifying zero-day threats and polymorphic malware that traditional antivirus solutions might miss. AI-powered systems constantly evolve to changing security environments, improving detection accuracy over time while reducing false alarms that could interfere with normal business activities.
Fine-grained Management Of Network Access
Administrators can set detailed rules governing which applications, services, and processes are permitted to connect to network resources, developing custom security policies aligned with organizational requirements. This detailed access control extends to individual ports, protocols, and IP addresses, verifying that even authorized applications run within strictly specified boundaries.
Role-based access controls allow organizations to implement different security policies for multiple user categories and departments, striking a balance between security needs with operational efficiency. By limiting network connectivity based on user identity, device type, and application context, businesses preserve operational efficiency while preventing unauthorized data exfiltration or harmful actions from compromised endpoints.
Benefits of Deploying Device Level Blocking Software
Organizations that utilize endpoint-based blocking solutions achieve comprehensive control over their network security posture, minimizing vulnerabilities and preventing unauthorized access at the source.
- Blocks malware activation before network penetration
- Decreases attack surface throughout all connected devices
- Improves adherence to regulatory requirements
- Lowers response duration and recovery costs
- Delivers detailed insight into endpoint activities
- Stops zero-day threats via behavioral analysis
By adopting these protective measures, businesses can substantially strengthen their cybersecurity framework while preserving operational efficiency and defending critical assets from growing threats.
How to Pick and Set Up Device -Level Blocking Software
Choosing the right endpoint protection solution demands thorough evaluation of your organization’s distinct security posture, infrastructure complexity, and operational requirements. Begin by performing a comprehensive assessment of your current threat landscape, identifying potential vulnerabilities across all device types, and establishing which critical assets require the greatest degree of protection to maintain business continuity.
The deployment process should utilize a structured rollout plan, beginning with pilot testing in non-critical environments before rolling out across the entire network. Establish clear guidelines regarding software allowlists and denylists, implement automated incident response protocols, and confirm that all stakeholders understand their roles in upholding a secure system environment throughout the deployment cycle.
Assessing Your Security Network Demands
A thorough security audit creates the foundation for choosing suitable content filtering tools, examining network topology, user behavior patterns, information classification, and compliance obligations. Record all endpoints including mobile devices, computers, servers, and connected devices to determine the complete range of protection needed across your network infrastructure.
Think about growth capacity as your business scales, ensuring the selected solution can accommodate increasing device counts and emerging threat landscapes. Review vendor capabilities for real-time threat intelligence updates, platform interoperability, and fine-grained control capabilities that match your specific industry regulations and internal security policies.
Integration with Current Security Infrastructure
Successful execution depends on seamless integration with your existing security stack, including firewalls, intrusion detection systems, SIEM platforms, and identity management solutions. Verify that the blocking software enables standard protocols and APIs for information sharing, enabling centralized visibility and coordinated response across all security layers within your infrastructure.
Test compatibility thoroughly in a controlled environment before deploying to production, guaranteeing that legitimate business applications remain operational without downtime. Establish clear communication channels between security tools through automated workflows, permitting incident data to flow efficiently and enabling security teams to correlate events for quicker threat identification and remediation.
Essential Guidelines for Regular Administration
Regular policy assessments and modifications are essential to ensure optimal performance as your security environment changes and organizational needs shift. Schedule quarterly assessments of blocking rules, removing outdated restrictions while adding new protections based on new security risks, user feedback, and threat investigation findings to maintain your protections up-to-date and effective.
Deploy comprehensive monitoring and reporting tools to monitor blocked activities, examine behaviors, and assess security enhancements over time. Offer ongoing training for support personnel and staff members, set up formal escalation protocols for false positives, and keep comprehensive records of all configuration changes to guarantee uniform application and rapid troubleshooting capabilities.
Comparing Device Level Block Management Solutions
When reviewing endpoint protection options, organizations must consider various factors including implementation difficulty, resource needs, management features, and overall effectiveness against new threats.
| Solution Type | Deployment Method | Management Overhead | Threat Coverage |
| Application Whitelisting | Agent-based deployment | Medium – requires regular updates | High for recognized applications |
| Network Access Controls | Infrastructure-based integration | High – complicated rule configuration | Medium – network layer only |
| Endpoint Detection Response | Cloud-based agents | Low – automated responses | Very high – behavior-based detection |
| Host Firewall | OS-native or third-party | Medium – policy setup | Medium – port-level control |
| Integrated Blocking Platform | Centralized distribution | Low – single unified dashboard | Comprehensive – multi-layered |
The best strategy integrates multiple protection layers, making sure that if one security layer fails, additional measures remain active to prevent compromise and preserve network integrity across your business.
Contemporary unified solutions offer centralized visibility and control, minimizing operational overhead while providing superior protection compared to standalone tools that demand separate management and coordination efforts.
Popular Questions
What is the distinction between device level blocking software and network firewalls?
While network firewalls operate at the network perimeter to monitor and control incoming and outgoing traffic between networks, device level blocking operates directly on individual endpoints such as computers, laptops, and mobile devices. Network firewalls examine packets based on IP addresses, ports, and protocols to determine whether traffic should be allowed or blocked at the network boundary. In contrast, endpoint-based blocking solutions function at the application and process level on each device, controlling which programs can execute, what resources they can access, and what network connections they can establish. This means that even if malicious traffic bypasses the network firewall, the endpoint protection can still prevent harmful applications from running or communicating. Additionally, device level solutions provide protection when devices are outside the corporate network, such as when employees work remotely or connect to public Wi-Fi networks, whereas traditional network firewalls only protect traffic passing through the network perimeter. The most effective security strategy employs both approaches in a layered defense architecture, with network firewalls providing the first line of defense and endpoint protection serving as a crucial secondary barrier that safeguards individual devices regardless of their location or network connection status.
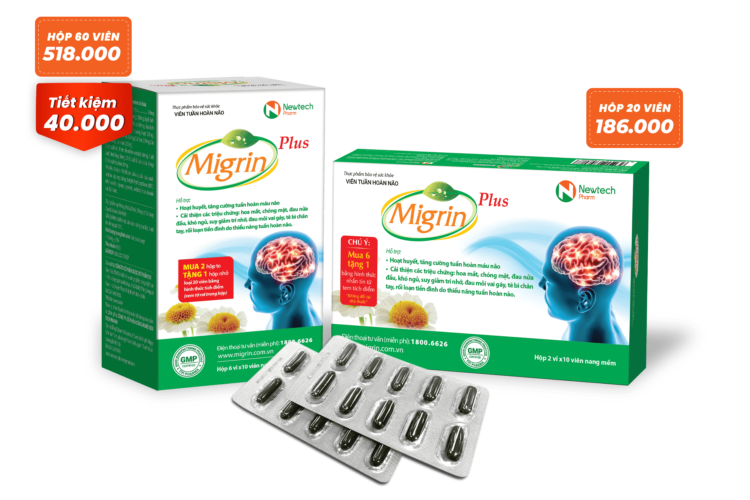


186,000/hộp 20 viên
518.000/hộp 60 viên
Cách dùng
2 viên/ lần x 2 lần/ ngày trong 3 tháng
3 lý do nên lựa chọn Migrin Plus