
In today’s digital environment, network protection has become a critical concern for companies of every size. As cyber threats grow more sophisticated, traditional perimeter defenses are inadequate to protect sensitive data and systems. Deploying instant withdrawal casino uk provides an critical security layer by managing what programs and tools can connect to your systems at the individual device level, effectively blocking harmful data before it can compromise your systems.
What Is Device Level Content Filtering and How It Functions
Advanced endpoint protection solutions work via monitoring and controlling network access at the individual device level, creating granular security policies that prevent unauthorized applications, websites, and services from connecting to corporate resources. This approach contrasts with traditional network firewalls by concentrating on what happens inside each device rather than just at the network perimeter, allowing administrators to create detailed rules for every device connected to their infrastructure.
The solution works by deploying lightweight agents on each endpoint that regularly monitor for suspicious activity, enforce access policies, and prevent connections that violate established security rules. These agents connect to centralized management consoles, enabling IT teams to deploy updates, modify policies, and respond to threats across thousands of devices simultaneously without requiring physical access to each machine.
By analyzing application behavior, network requests, and file operations in real time, these security solutions can identify and stop threats such as malicious software, ransomware, phishing attempts, and data exfiltration before they propagate through the network. The system maintains detailed logs of all blocked activities, offering critical intelligence for security audits and helping organizations understand their threat landscape while maintaining adherence with industry regulations.
Key Security Threats That Device-Level Blocking Software Blocks
Current networks face an constantly changing array of security threats that can jeopardize data integrity, disrupt operations, and damage organizational reputation. By deploying security solutions at the endpoint, organizations can effectively neutralize threats before they advance further into the network infrastructure. This preventive strategy creates several layers of protection against malicious actors attempting to leverage security gaps.
Comprehending the distinct kinds of threats that device-level protection addresses helps organizations recognize the extensive security advantages. From stopping malicious software execution to stopping illicit communication efforts, this security mechanism serves as a essential defensive tool. The following sections explore the key threat classifications that this solution successfully addresses.
Malware and Ransomware Security
Malware infections pose one of the most widespread and destructive security threats affecting businesses today. Ransomware attacks, in particular, have surged significantly, encrypting critical files and requiring ransom for their release. Device-level blocking stops harmful programs from running and halts unauthorized activity from connecting to command-and-control servers, effectively neutralizing these threats at their source.
By monitoring application behavior and blocking unauthorized software installations, this security solution prevents malware from gaining a foothold on networked systems. Real-time threat detection identifies suspicious activities such as unexpected file changes or unexpected network connections. This immediate response capability substantially decreases the window of opportunity for malware to spread across the network and create extensive harm.
Phishing and Social Media-based Attacks
Phishing schemes exploit human psychology to manipulate users into revealing sensitive information or downloading malicious content. These sophisticated schemes often bypass traditional email filters by using legitimate-looking communications. Device-level protection restricts entry to known phishing sites and prevents malicious attachments from executing, even when users inadvertently click on dangerous links or view suspicious files.
Social engineering tactics continually change, making user education alone inadequate for complete protection. Automated blocking mechanisms identify and prevent connections to fraudulent websites and malicious domains in real-time. This technical safeguard supports security awareness training by providing a safety net that protects against momentary lapses in judgment, markedly lowering the success rate of these deceptive attacks.
Unauthorized Access and Information Leaks
Illicit access attempts create major threats to organizational data security and regulatory compliance. Attackers persistently monitor networks for vulnerabilities, seeking entry points to extract sensitive information or gain persistent access. Device-level controls control which applications can communicate externally, and track for unusual access patterns, effectively preventing unauthorized data exfiltration and blocking suspicious access requests.
Data breaches often result from exposed login information and exploited software vulnerabilities that enable attackers to move laterally within networks. By implementing rigorous application restrictions and monitoring device behavior, this security approach limits the potential damage from compromised accounts. Even if attackers gain initial access, they encounter extra safeguards that prevent them from accessing sensitive resources or transmitting stolen data outside the network perimeter.
Advantages of Implementing Device Level Blocking Software
Organizations gain improved protection capabilities by implementing blocking solutions at the device level, which establishes granular protection across every endpoint in the network. This approach ensures that each workstation, mobile device, and IoT component functions within established security guidelines, blocking unauthorized applications from executing or communicating externally. The result is a substantially diminished attack surface that makes it exponentially more difficult for threat actors to establish footholds within your infrastructure.
Administrative efficiency improves dramatically when security policies are enforced directly on devices rather than relying solely on network-level controls. IT teams can deploy consistent security configurations across diverse device types and operating systems, ensuring uniform protection regardless of where employees work or how they connect. This centralized management capability reduces the complexity of maintaining security standards while providing real-time visibility into potential threats and compliance violations across the entire organization.
Cost reductions come from avoiding security events before they escalate into costly data compromises or system downtime. By blocking malicious software and unauthorized network connections at the source, organizations avoid the substantial financial impact of incident response, regulatory fines, and reputational impact. The proactive strategy of device protection also reduces the burden on security staff, enabling them to concentrate resources on key priorities rather than perpetually reacting to avoidable risks.
Best Practices for Implementing Device Level Blocking Software
Effective deployment of endpoint protection necessitates strategic planning and adherence to established security protocols. Organizations should establish thorough deployment approaches that correspond to their particular network infrastructure, business requirements, and compliance obligations to maximize protection effectiveness.
Setup and Policy Management
Setting up comprehensive, clearly defined guidelines creates the cornerstone of strong endpoint protection. Security administrators must establish detailed rules that specify which software programs, web resources, and network resources are allowed or restricted for distinct user populations and device classes in line with organizational needs.
Regular policy evaluations and updates guarantee security configurations remain aligned with changing organizational needs and new security risks. Organizations must establish role-based permission systems and maintain detailed documentation of all policy changes for compliance and auditing and problem resolution.
Consistent Updates and Monitoring
Maintaining current threat definitions and application versions is critical for protecting against the latest security vulnerabilities. Organizations should implement automatic update routines while testing patches in controlled environments before complete rollout across production systems.
Continuous monitoring of intercepted threats, network traffic patterns, and system logs enables security teams to identify potential issues rapidly. Deploying immediate alert systems and performing periodic security audits help organizations respond proactively to unusual behavior and strengthen their protection strategies.
Picking the best device-level blocking tool for Your Network
Selecting the appropriate security tool requires thorough assessment of your company’s particular security requirements, system architecture, and practical considerations. Evaluate factors such as the range and kinds of endpoints accessing to your infrastructure, the sensitivity of data being safeguarded, and your team’s technical expertise. A detailed analysis of these components will assist in determining which features and capabilities are most important for your organization.
Compatibility with your existing security infrastructure is paramount when assessing different solutions. The blocking software should function efficiently with your current firewalls, intrusion detection systems, and endpoint protection platforms. Look for solutions that accommodate your operating systems and device types while offering centralized management capabilities that ease policy enforcement across your entire network.
Operational efficiency and growth capacity must match your network’s demands to prevent bottlenecks that could impact business operations. Assess whether the solution handles peak traffic loads and whether it can scale alongside your organization. Obtain detailed performance metrics and conduct pilot tests to ensure the software preserves network performance while delivering strong security without introducing latency issues.
Vendor reputation, technical assistance quality, and update frequency are crucial considerations that impact sustained security performance. Investigate the provider’s track record in responding to emerging threats and their commitment to regular updates. Ensure they provide detailed documentation, training resources, and reliable technical assistance to enable your organization maximize the solution’s protective capabilities and quickly address any implementation challenges.
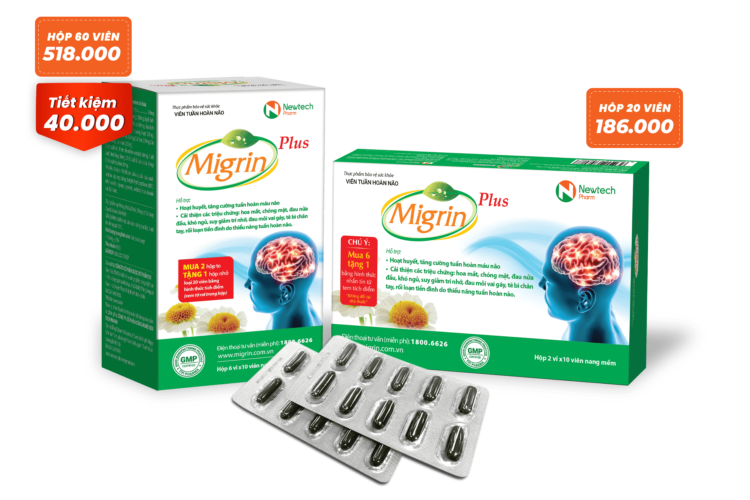


186,000/hộp 20 viên
518.000/hộp 60 viên
Cách dùng
2 viên/ lần x 2 lần/ ngày trong 3 tháng
3 lý do nên lựa chọn Migrin Plus